Skip to Content

Review and implementation

Review security headers. Improve your website with purpose.

Missing or unsuitable security headers can leave additional browser protections unused. Appropriate rules make certain attacks involving injected scripts or malicious framing harder. We explain your specific findings, assess their possible consequences and improve the configuration with agreed functional tests.

Remote support throughout Germany. On-site appointments in Wunstorf and the Hanover region by arrangement.

Our own work, documented clearly

Settings produce visible results.

These excerpts show documented test results from our own websites. Each result includes its address and time. They show the development of header grades, rather than a comprehensive security audit or an isolated A/B experiment.

Lopez IT Welt: from D to A+

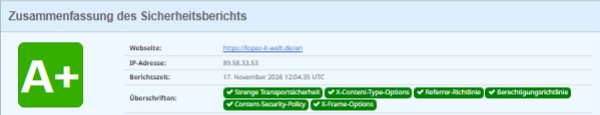
The two reports show documented progress: D on 29 October and A+ on 17 November 2026. Between these dates, the primary address changed from www to the address without www. These are dated results for our own website, rather than evidence of a single change tested in isolation.
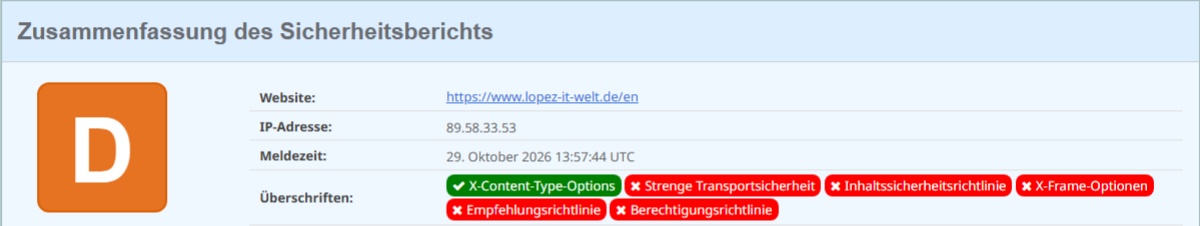
Earlier documented resultD29 October 2026 · 14:57:44 CET
Security Headers excerpt: Lopez IT Welt, grade D, 29 October 2026 at 14:57:44 CET.Enlarge report excerpt
Later documented resultA+17 November 2026 · 13:04:35 CET
Security Headers excerpt: Lopez IT Welt at https://lopez-it-welt.de/en, grade A+, 17 November 2026 at 13:04:35 CET.Enlarge report excerpt

Earlier tested address: https://www.lopez-it-welt.de/en · Address tested on 17 November 2026: https://lopez-it-welt.de/en
Another website we own: Lopez Marketing GmbH

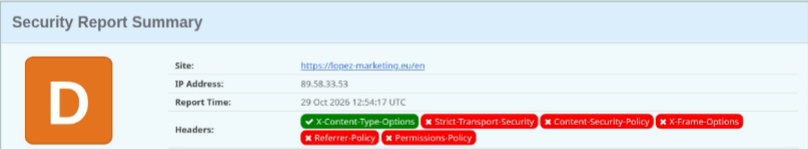
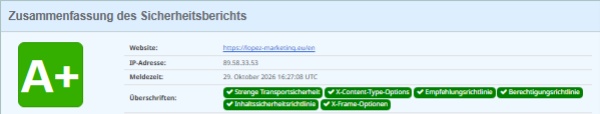
Our own marketing company’s website also has documented results for the same endpoint: D and later A+ on 29 October 2026. This is one of our own company websites, not an external customer reference.

Earlier documented resultD29 October 2026 · 13:54:17 CET
Security Headers excerpt: our own Lopez Marketing GmbH, grade D, 29 October 2026 at 13:54:17 CET.Enlarge report excerpt
Later documented resultA+29 October 2026 · 17:27:08 CET
Security Headers excerpt: the same marketing endpoint, grade A+, 29 October 2026 at 17:27:08 CET.Enlarge report excerpt

Address tested in both reports: https://lopez-marketing.eu/en

Each report applies to the stated address and test time. The grade evaluates selected HTTP headers. It does not certify the security of every page, account or business process.

What security headers do for your website

Use HTTPS consistently with HSTS

After receiving a valid HSTS policy, the browser uses HTTPS for the covered domain. This makes falling back to unencrypted HTTP connections harder; data sent over HTTP can be read or altered. The policy lifetime and included subdomains must fit the infrastructure.

Restrict injected scripts with CSP

An appropriate Content Security Policy restricts which scripts and content the browser may load or execute. It provides an additional defence if an attacker exploits a vulnerability to inject code. Such code can modify page content or access data. Secure development remains essential.

Make malicious framing harder

The CSP frame-ancestors directive determines who may embed your page. It helps defend against clickjacking, where hidden or overlaid controls trick visitors into unintended clicks. We account for required portals and integrations when configuring the rules.

From findings to tested changes

You receive an understandable basis for a decision and a clearly defined next step.

  1. Record the current state

    Document the address, time, delivered headers and noteworthy values.

  2. Consider the functions

    Account for forms, login, shop, external services and necessary embedding.

  3. Agree the change

    Agree the scope and required access. A CSP can first be observed in Report-Only mode: violations are reported when a reporting endpoint is configured, but this policy does not yet block them. We then agree the configuration to enforce.

  4. Demonstrate the result

    Test affected workflows and document the headers and results before and after the change. We check that the agreed protection rules are delivered and that important functions such as forms, login and the shop still work.

Matched to the actual need

Even an information website benefits from appropriate browser protection rules. Shops, logins and sensitive data require particularly careful assessment of the possible consequences of an attack. We prioritise findings according to functions, data and impact. The test grade provides one documented part of the evidence; it is not a comprehensive or permanent security guarantee.

A header review does not replace a comprehensive security audit or legal assessment. Additional tasks are agreed as a separate scope.

  • An understandable overview of the tested header configuration
  • Recommendations specific to your website
  • Implementation of explicitly agreed changes
  • Functional tests and documented results

Frequently asked questions

My website uses HTTPS. Why review headers as well?

HTTPS protects data in transit. On its own, it prevents neither injected scripts nor malicious framing. An appropriate CSP and framing rules add protection; after a valid policy has been received, HSTS maintains HTTPS use. We review the specific report to establish which rules your website needs.

Does F mean my website has already been attacked?

No. F does not establish that an attack or damage has already occurred. The lowest test grade is, however, a clear signal to examine the tested header configuration for missing or unsuitable protection rules. Depending on the findings, additional browser rules that hinder certain script attacks or malicious framing may be absent. The actual possible consequences also depend on existing vulnerabilities and website functions. We assess the findings and test agreed improvements.

Does every website need A+?

Not every website needs the same configuration. A shop with customer accounts and payments has different workflows and data to protect from an information website. Appropriate basic protection rules are useful there too. A high header grade can be one objective; effective settings and working features are what matter. A+ alone does not establish that an entire website is secure.

What do you need for an initial discussion?

The website address and a brief indication of whether you want a review or implementation support. Mention important functions such as a shop, login or external services. Please do not send passwords or access codes at this stage.

Let us make sense of your findings.

Send us the website address or an existing report link and briefly describe your goal. We will discuss an appropriate next step with you.

Sources and image attribution

Technical background:

Report excerpts: Security Headers by Snyk. Licensed under CC BY-SA 4.0. The excerpts have been cropped; the grades have not been altered. Reproduction does not imply endorsement by the testing service.

View licence